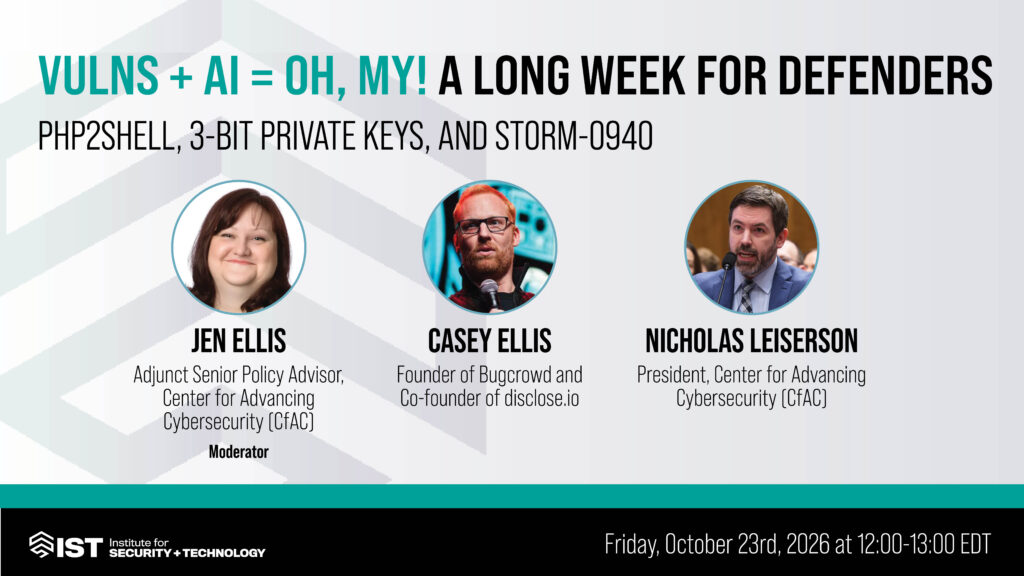
Between two remote code execution PHP vulnerabilities, the discovery of easy-to-access keys issued by an Indian certificate authority, and new reports of a China-state aligned hacking campaign that leveraged AI, it's been a long week for cyber defenders. What should policymakers take away from this week? Is this a manifestation of the so-called “AI-powered vulnpocalypse” that has been heralded over the past year?
It’s been a long week for cyber defenders. Two critical vulnerabilities in PHP could affect up to 70% of all websites, and governments have been urging operators to either patch or go dark. Exacerbating the stress for website owners, researchers disclosed that an Indian certificate authority has been using easy-to-guess keys that enable malicious actors to impersonate valid servers in order to intercept traffic. This could affect more than 60 million websites. Rounding out the week, Microsoft reported on a China-state aligned hacking campaign that leveraged agentic AI to increase the speed and scale of exploitation.
What should policymakers take away from this week? Is this a manifestation of the so-called “AI-powered vulnpocalypse” that has been heralded over the past year? What does clean up look like across each of these three distinct incidents (not to mention LiteLLM and the Node.js vulnerability)? Join experts from IST’s Center for Advancing Cybersecurity and the broader ecosystem as we unpack the week that was.
Panelists:
Casey Ellis, Founder of Bugcrowd and Co-founder of disclose.io
Jen Ellis, Adjunct Senior Policy Advisor, Center for Advancing Cybersecurity (CfAC)
Nick Leiserson, President, Center for Advancing Cybersecurity (CfAC)